


Framework Laptop 13 11th Gen Intel® Core™ — BIOS 3.25
Downloads
Section titled “Downloads”- Updated Intel SIC to 8063.00.
- Updated CSME to 15.0.55.2751v6 Corporate.
- Update Microcode to 0xBE.
- Added support for Framework Laptop 13 Pro features - Enabled compatibility for the haptic touchpad, touch panel, and 74W battery.
- Fixed an issue where the system was unable to boot from partially locked self-encrypting drives (SEDs)
- Fixed an issue where the Battery Extender status was reported incorrectly following a reboot, hibernation, or shutdown after the timer had expired.
- Enhanced the Power On AC behavior, allowing the feature to work correctly without requiring the system to boot into the Operating System at least once for initialization.
- Secure Fix: CVE-2025-32008 - Out-of-bounds write in the firmware for the Intel(R) AMT and Intel(R) Standard Manageability within Ring 3: User Applications may allow a denial of service. Network adversary with an unauthenticated user combined with a low complexity attack may enable denial of service. This result may potentially occur via network access when attack requirements are not present without special internal knowledge and requires no user interaction. The potential vulnerability may impact the confidentiality (none), integrity (none) and availability (high) of the vulnerable system, resulting in subsequent system confidentiality (none), integrity (none) and availability (low) impacts. (CVSS 8.6)
- Secure Fix: CVE-2025-20080 - Null pointer dereference in the firmware for some Intel(R) AMT and Intel(R) Standard Manageability within Ring 0: Kernel may allow a denial of service. Network adversary with an unauthenticated user combined with a high complexity attack may enable denial of service. This result may potentially occur via network access when attack requirements are present without special internal knowledge and requires no user interaction. The potential vulnerability may impact the confidentiality (none), integrity (none) and availability (high) of the vulnerable system, resulting in subsequent system confidentiality (none), integrity (none) and availability (none) impacts. (CVSS 6.8)
- Secure Fix: CVE-2025-27708 - Out-of-bounds read in the firmware for some Intel(R) Converged Security and Management Engine (CSME) Firmware (FW) within Ring 0: Kernel may allow an information disclosure. System software adversary with a privileged user combined with a low complexity attack may enable data exposure. This result may potentially occur via local access when attack requirements are present without special internal knowledge and requires no user interaction. The potential vulnerability may impact the confidentiality (high), integrity (none) and availability (none) of the vulnerable system, resulting in subsequent system confidentiality (none), integrity (none) and availability (none) impacts. (CVSS 4.1)
- Secure Fix: CVE-2025-31648 - Improper handling of values in the microcode flow for some Intel(R) Processor Family may allow an escalation of privilege. Startup code and smm adversary with a privileged user combined with a high complexity attack may enable escalation of privilege. This result may potentially occur via local access when attack requirements are present with special internal knowledge and requires no user interaction. The potential vulnerability may impact the confidentiality (low), integrity (low) and availability (none) of the vulnerable system, resulting in subsequent system confidentiality (low), integrity (low) and availability (none) impacts. (CVSS 3.9)
Component Versions
Section titled “Component Versions”This BIOS update is a bundle of updates to multiple embedded components in the system. Not all of them use the same version number.
| Component | Version | |
|---|---|---|
| EC | ec_325_e12d9a6 | Updated |
| PD | 3.4.0.2576 | |
| Intel CSME | 15.0.55.2751 | Updated |
| Microcode | 0xBE | Updated |
Windows Driver Component Versions
Section titled “Windows Driver Component Versions”| Driver | Version | |
|---|---|---|
| Intel Chipset | 10.1.20398.8776 | Updated |
| Intel GNA | 3.00.00.1457 | |
| Intel Management Engine | 2601.9.16.0 | Updated |
| Intel Serial IO | 31.100.2129.8 | |
| Intel Smart Sound | 10.29.00.9467 | |
| Intel Sensor Solution | 10.29.00.9467 | |
| Intel Display | 32.0.101.7085 | Updated |
| Intel Dynamic Tuning | 8.7.10802.26924 | |
| Realtek Audio | 6.0.9969.1 | Updated |
| Realtek Audio Console | 1.53.393.0 | Updated |
| Intel Thunderbolt | 1.41.1340.0 | |
| Intel PROSet WiFi | 24.30.1.1 | Updated |
| Intel PROSet Bluetooth | 24.30.1.1 | Updated |
| Goodix Fingerprint | 3.12804.1.290 | Updated |
| Realtek Ethernet | 11013_20_07272023_08042023 | |
| SD Card Reader | v4_5_10_201 |
Installation
Section titled “Installation”You can check your current BIOS version following the steps here to determine if you are on the latest release.
Framework firmware is published to LVFS and updates via fwupd, which ships by default on most modern distributions.
fwupdmgr refresh --forcefwupdmgr get-updatesfwupdmgr updateWindows
Section titled “Windows”- Download the Framework Laptop 13 11th Gen Intel® Core™ BIOS 3.25 Windows Installer.
- Run the
.exeand click "Yes" when prompted to reboot. - Wait for the firmware progress bar to complete — the system will reboot automatically. Do not interrupt.
- Download and install theWindows Driver Bundle v3.04 for your system if you are currently using a previous Driver Bundle release, or you are installing the Driver Bundle for the first time.
EFI Shell Update
Section titled “EFI Shell Update”- Download the EFI Shell Update v3.25.
- Extract contents of zip folder to a FAT32 formatted USB drive. Cleanly unmount the drive before physically removing it, otherwise the BIOS update may not function correctly.
- Attach a charger to your device while updating.
- Boot your system while pressing F12 and boot from the thumb drive.
- Let startup.nsh run automatically.
- Follow the instructions to install the update.
Updating a Mainboard without a Laptop
Section titled “Updating a Mainboard without a Laptop”This release supports standalone updates without a battery attached, but only when updating using the EFI shell method. After rebooting, please follow the onscreen instructions to update your BIOS when in standalone mode, which will require moving the power source between both sides of the Mainboard to allow PD firmware to update correctly.
We recommend the following update flow for standalone updates:
- Ensure that standalone operation is enabled in the BIOS advanced setup menu.
- Connect the display to the upper left port.
- Connect the power to the lower left port.
- Run the updater from the EFI shell, following the EFI Shell Update instructions above.
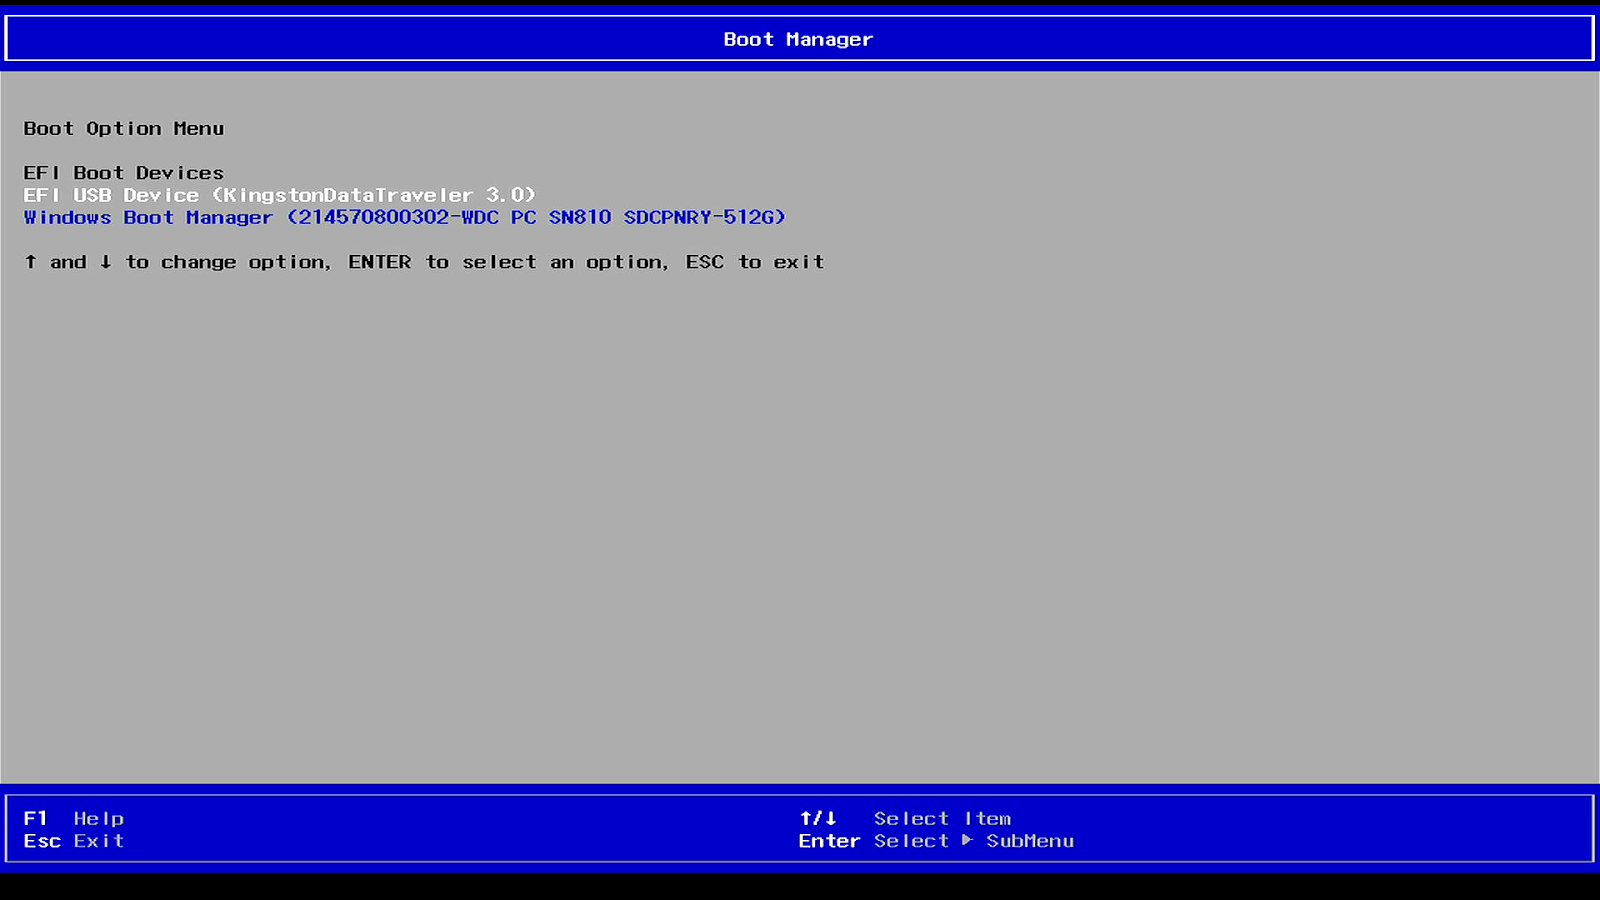
- Select the EFI USB Boot Device.
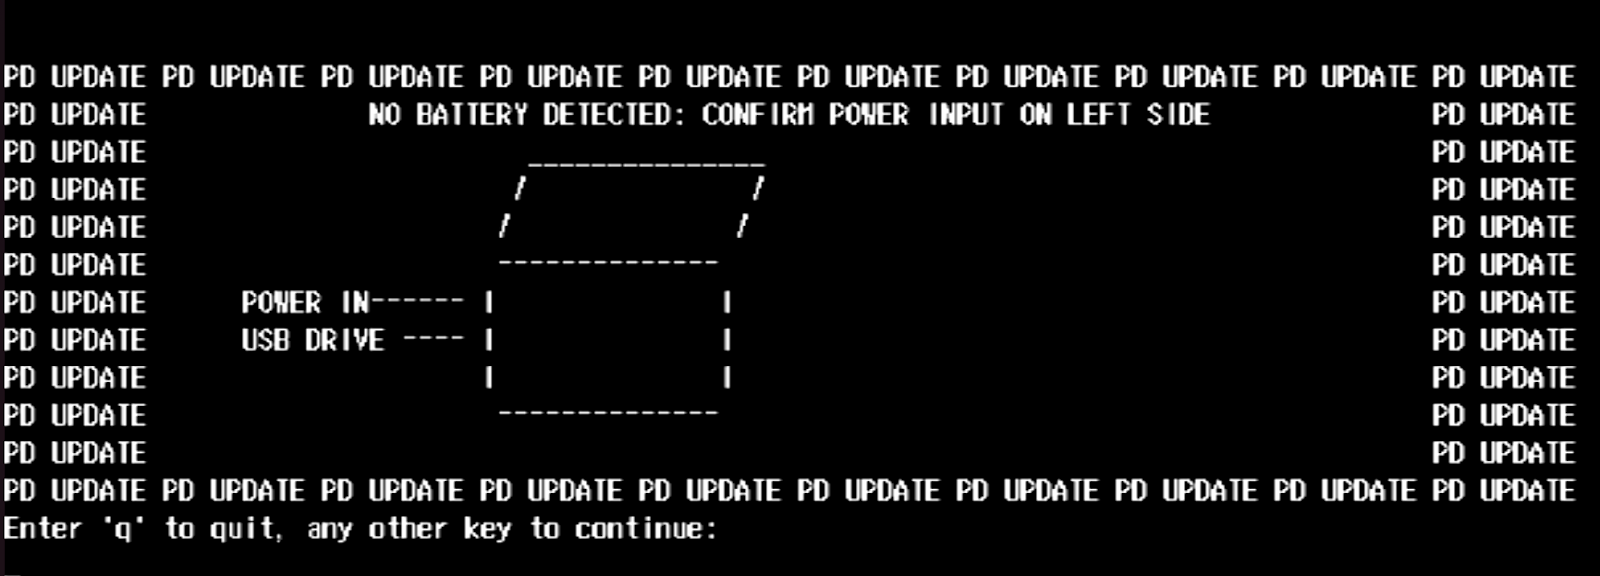
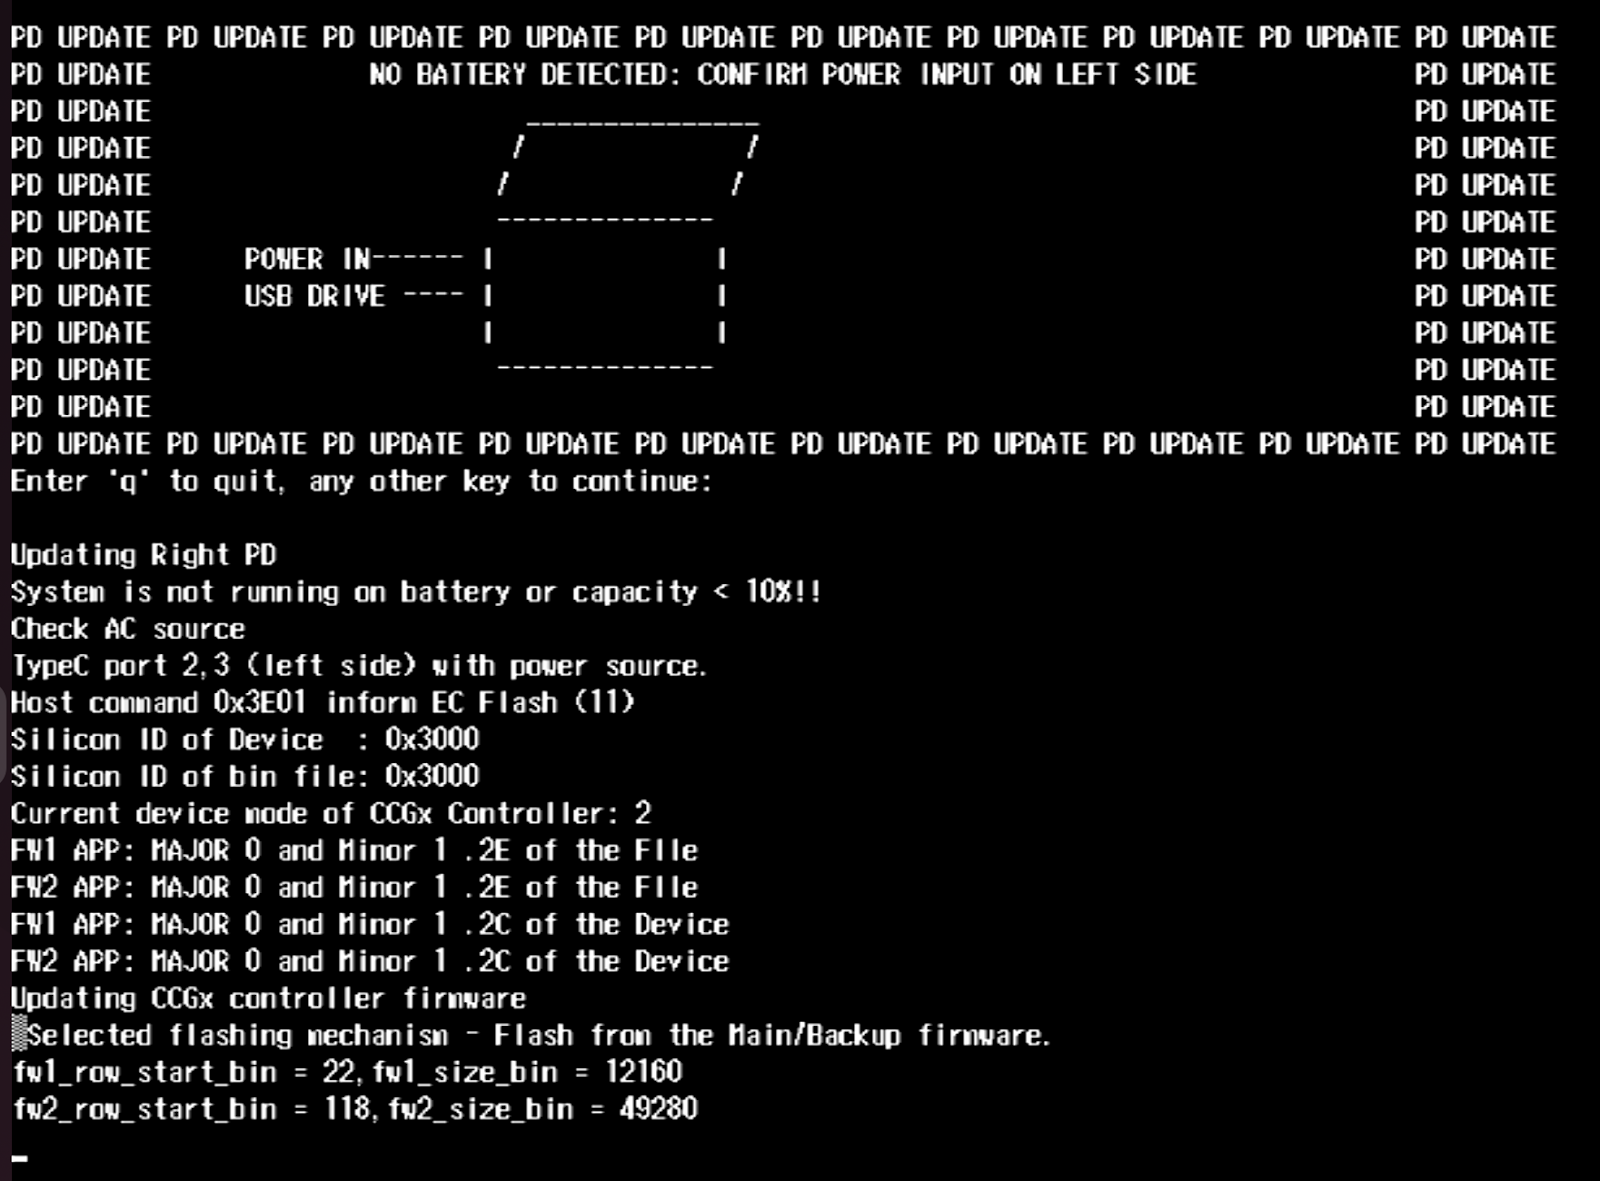
- The updater will update the PD controller on the right side. Press any key to continue updating.
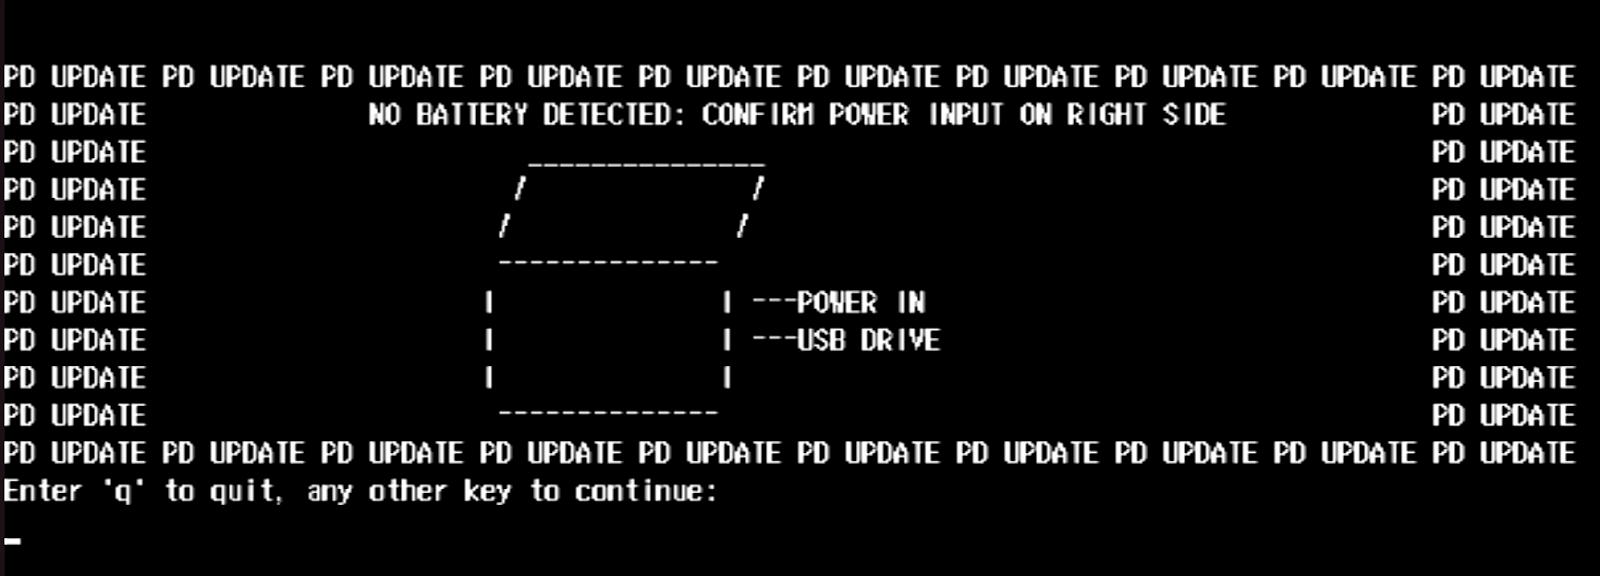
- Move the display to the upper right port and the power to the lower right port, then boot back into the EFI updater. The updater will update the PD controller on the left side. Press any key to continue updating.
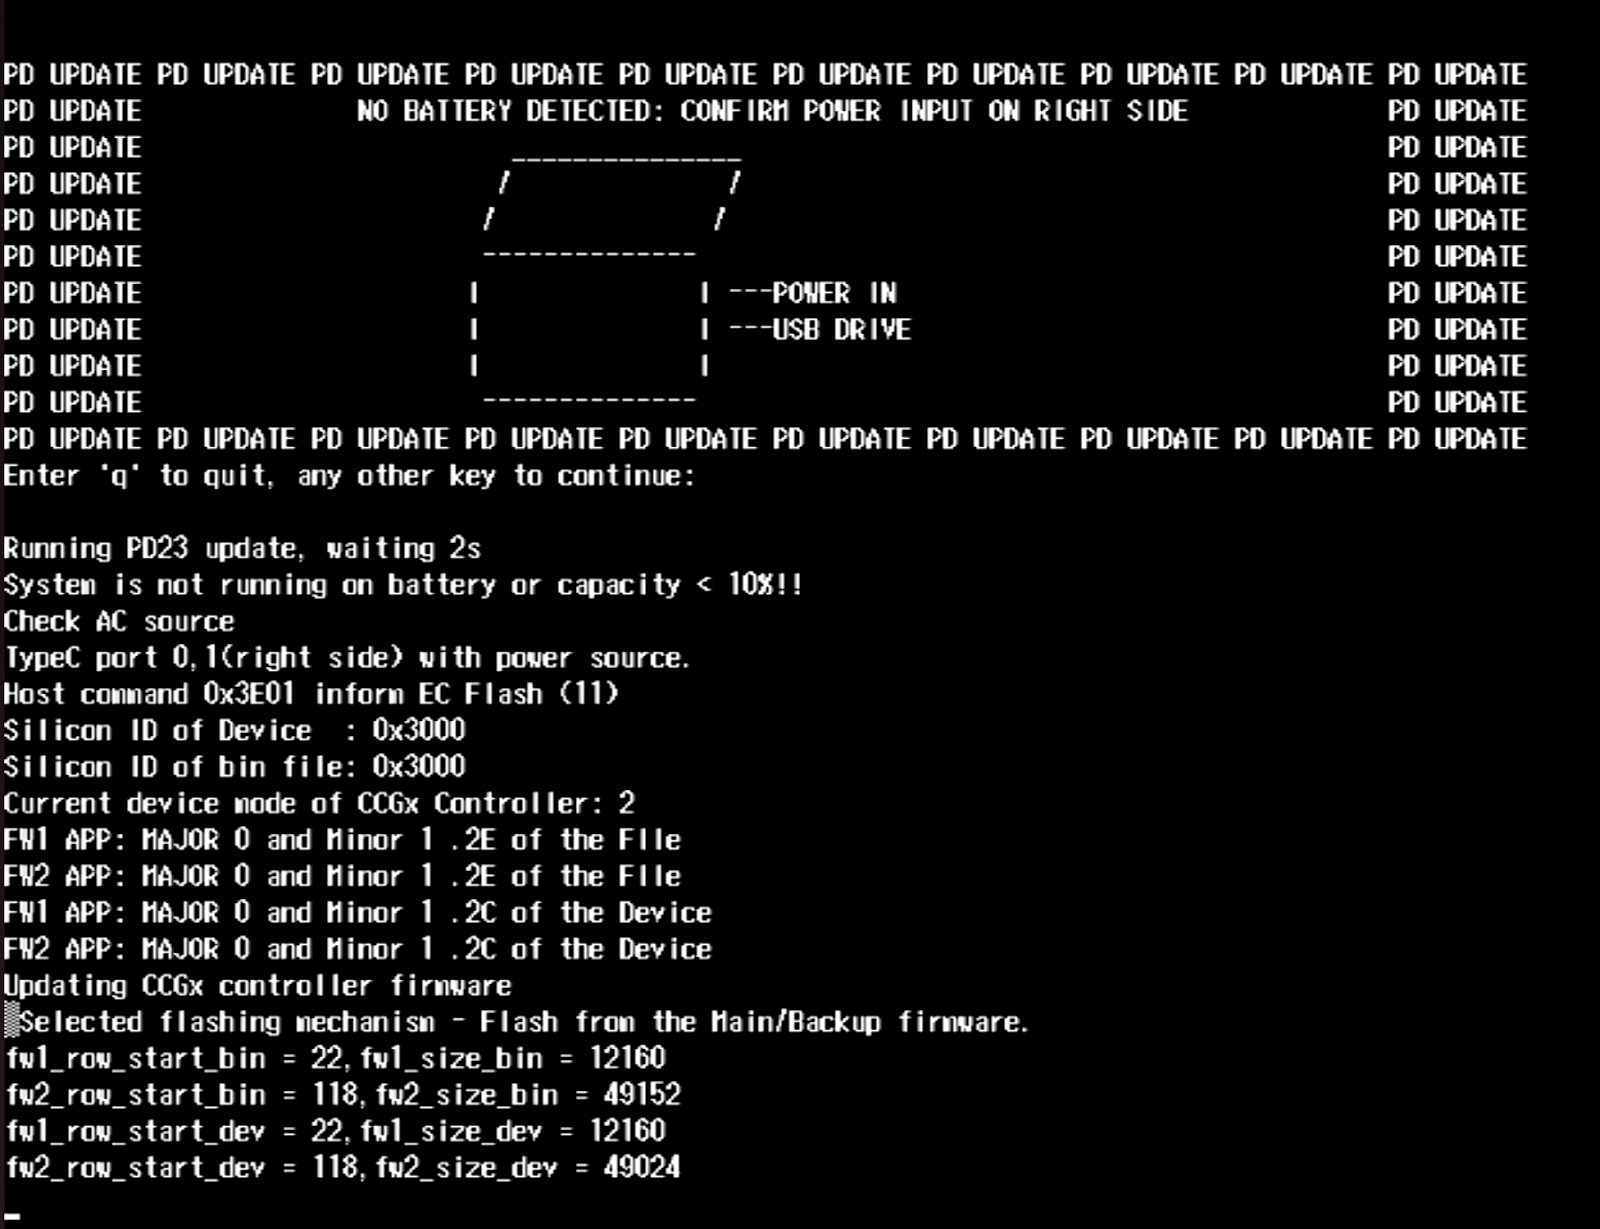
- After the PD updates finish, the system reboots automatically and starts the BIOS capsule update.
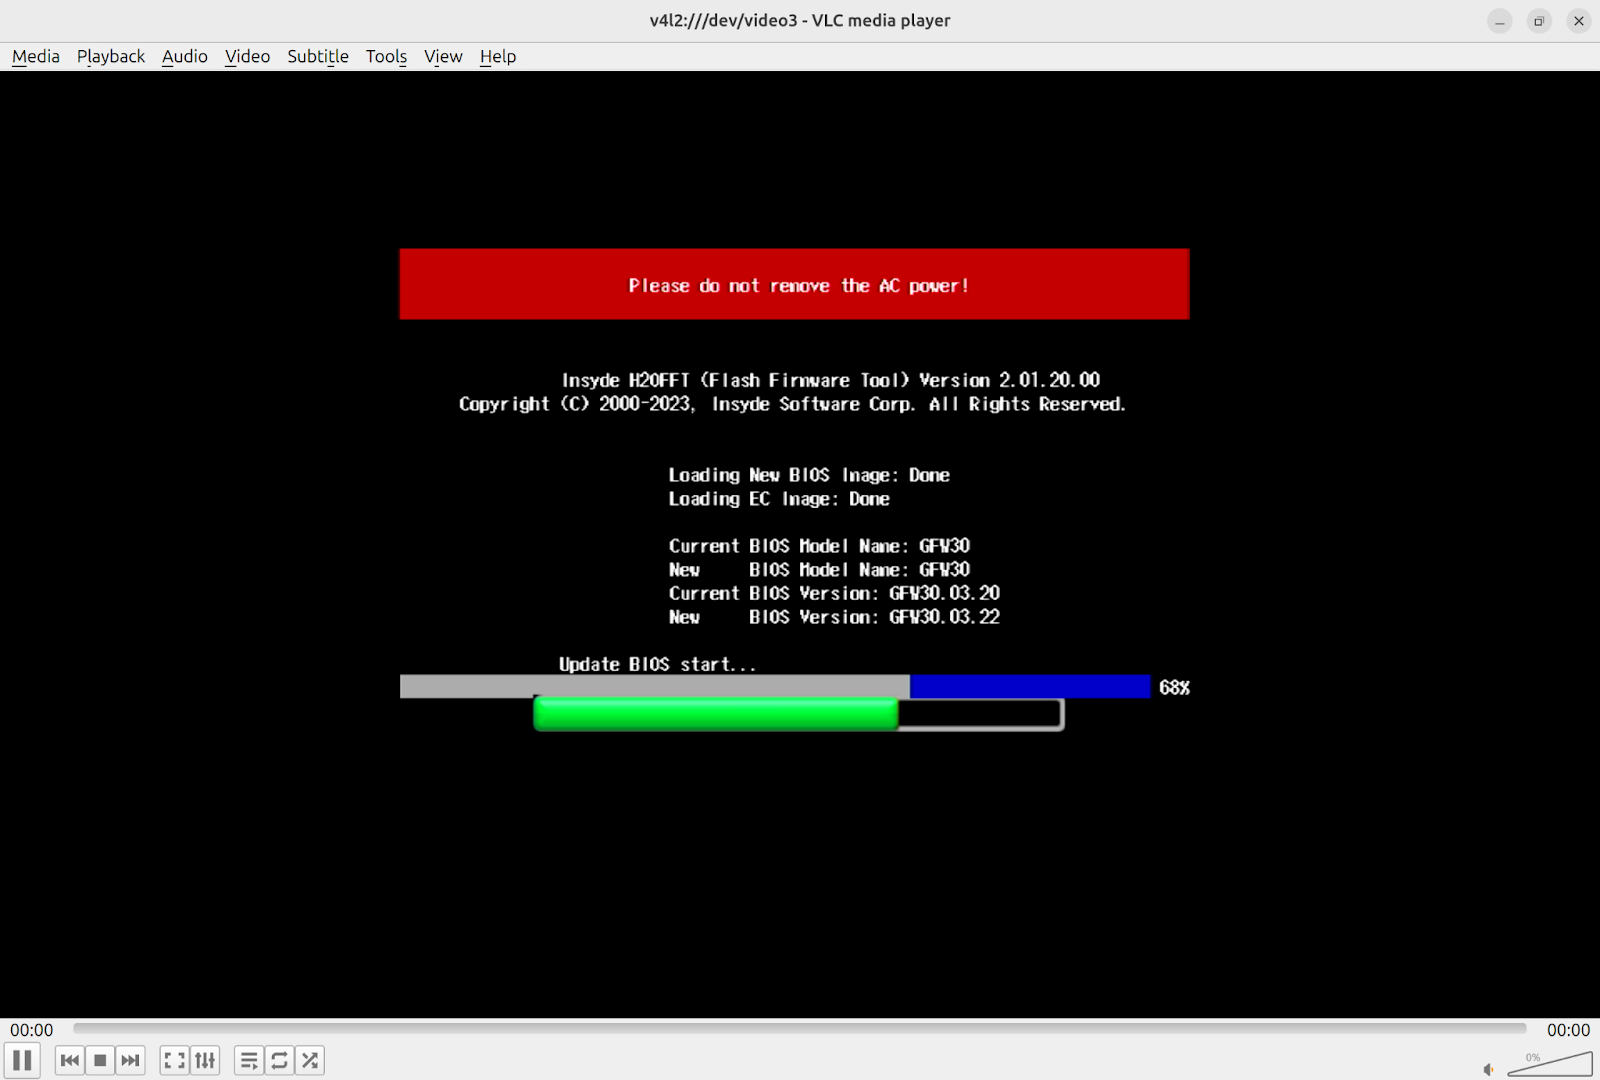
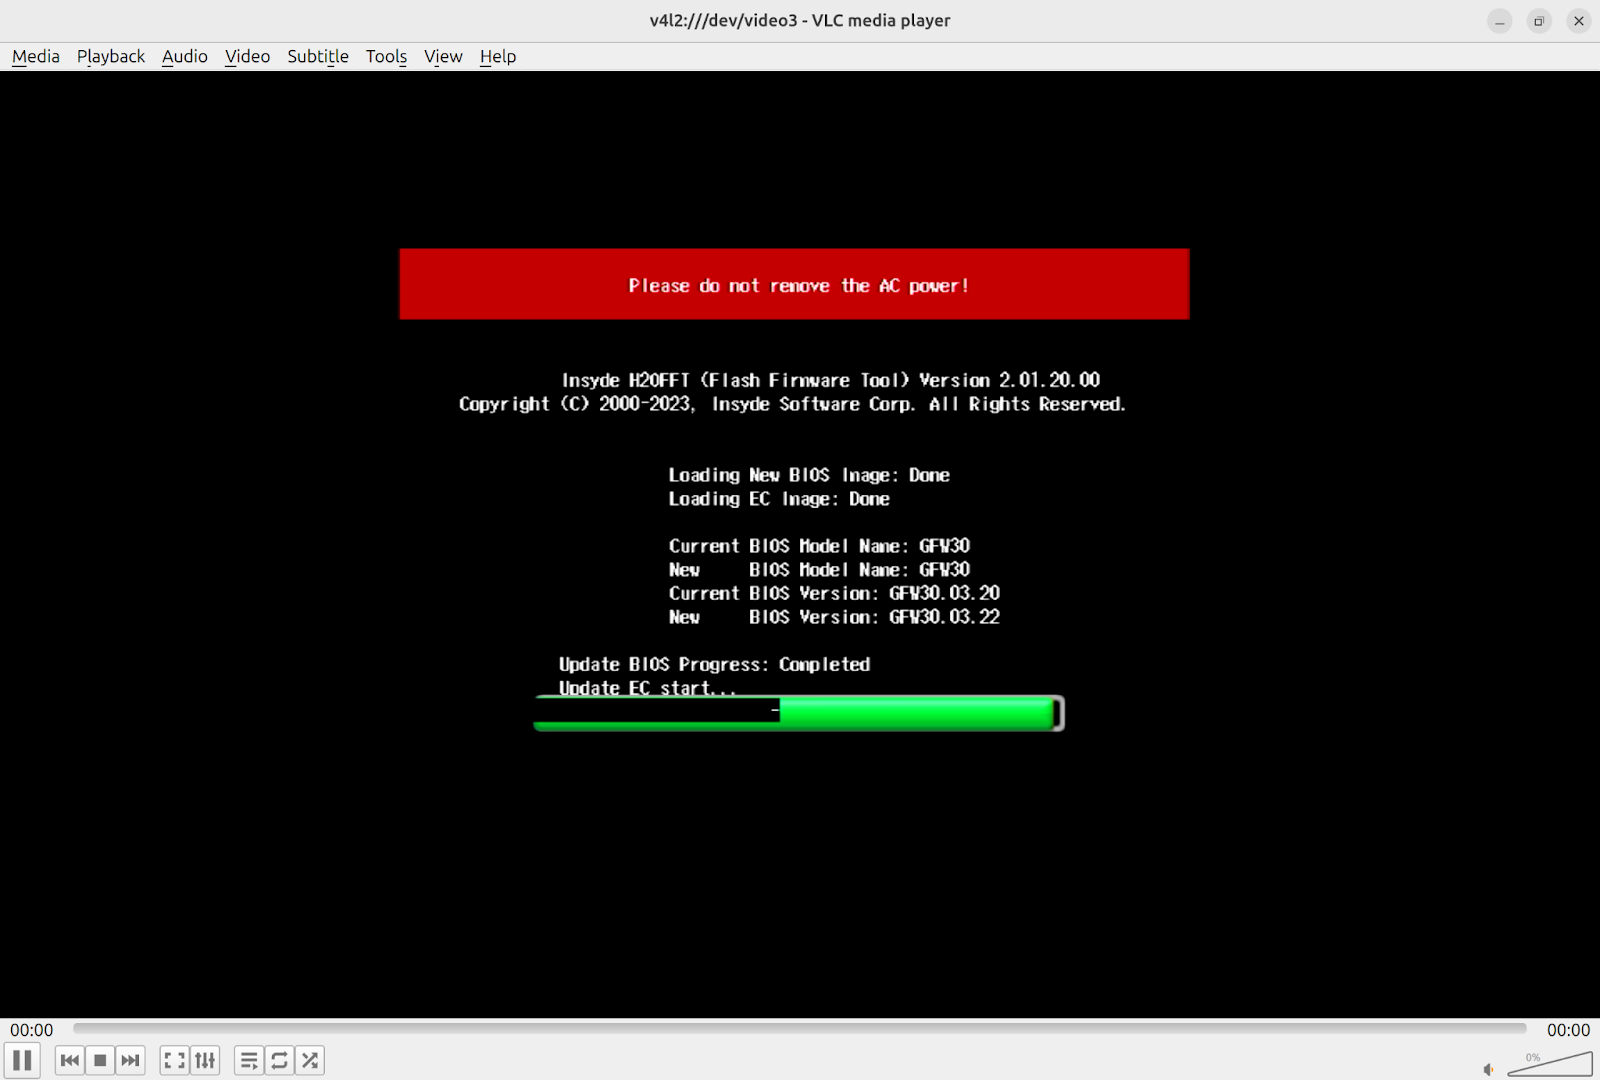
- The EC updates once the BIOS section finishes.
Known Issues
Section titled “Known Issues”- The EFI update will not work with filesystems formatted using MBR
- If you get a security violation during the EFI update, disable secure boot
- This update requires a battery present to complete the update
- Linux users have reported that S3 sleep no longer works
Reporting Issues
Section titled “Reporting Issues”Please use the public issue tracker on GitHub to report issues.
If you experience an issue with the update that is related to your system firmware, please post as complete a description as you can, including relevant system information and external peripherals. Please note that we do not currently have a SLA for responding to issues on github, but we will be reviewing them through the bios release process, and will review them for future updates as well.
Please contact support if you have an issue regarding hardware, broken devices, returns, etc.